BitLocker Recovery Key: How to Create, Find and Back It Up
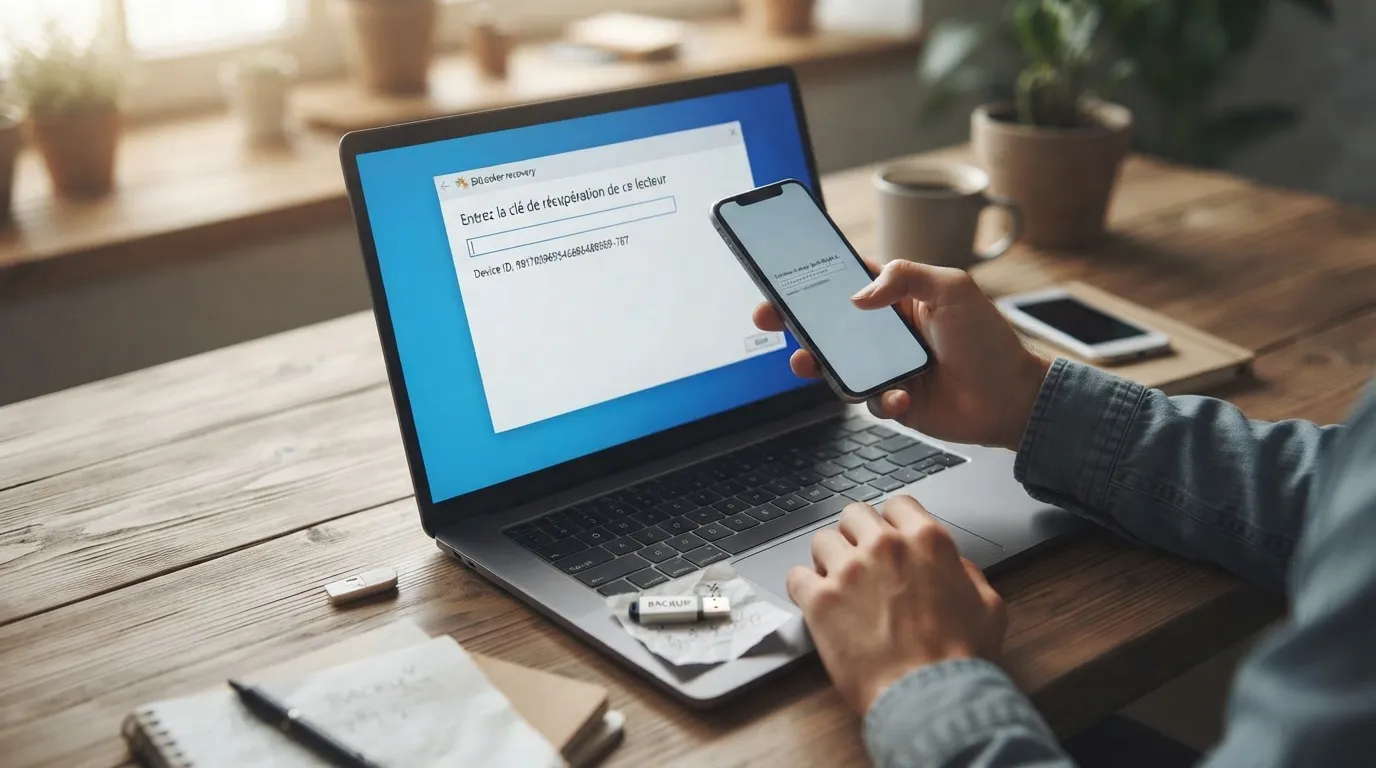
The BitLocker recovery key is the passcode that unlocks an encrypted drive when Windows doesn’t boot normally — after an update, a hardware change, a BIOS change or a TPM reset. Without it, your data is permanently inaccessible: that’s the very principle of encryption. This complete guide explains where to find it (all the possible sources), how to back it up properly, and how to generate one if you enable BitLocker. The goal: never get locked out again.
Who this guide is for: anyone with an encrypted Windows PC (BitLocker or « device encryption »), whether a home user or in a company, who wants to secure their key before an incident happens — or find it in an emergency.
Prerequisites: administrator access for some steps, a second device for the online search, and 10 minutes. No advanced skills required.

Understand the recovery key in one minute
The recovery key is a 48-digit numeric code, split into eight groups of six. It’s unique to each encrypted volume. When it asks for it, Windows shows a Key ID — a few characters — used to recognize the right key among several.
Good to know: this key does not open a Windows session; it’s a fallback mechanism that appears only when BitLocker detects an abnormal situation at startup. Normally, decryption is automatic thanks to the TPM chip.
Step 1: check whether your PC is encrypted (and by what)
Before hunting for a key, confirm that encryption is active. Open an admin command prompt and type:
manage-bde -statusThe « Protection status » line indicates whether protection is on. On Home editions, it’s often « Device Encryption, » a simplified version of BitLocker enabled automatically if you’re signed in with a Microsoft account. You can also check in Control Panel → BitLocker Drive Encryption (Pro editions) or Settings → Privacy & security → Device encryption (Home editions).
Step 2: find your recovery key (all the sources)
Go through these locations in order: the key is somewhere.
1. Your Microsoft account (the most common)
From another device, open aka.ms/myrecoverykey (or account.microsoft.com/devices/recoverykey) and sign in with the Microsoft account linked to the PC. Compare the Key ID on screen with the one on the site, then note the 48 digits.
Tip: try all your Microsoft accounts, including those of a relative who set up the machine. BitLocker saves the key to any account ever connected to the device.
2. Microsoft Entra ID (Azure AD) and Intune — work or school PCs
If the PC belongs to an organization, the key is almost always archived on the admin side. The user can view it at myaccount.microsoft.com → Devices; the administrator, in the Microsoft Entra admin center (Devices → the device → BitLocker recovery keys) or in Intune.
3. Local Active Directory
On an on-premises managed domain, the key is stored in the computer object (attribute msFVE-RecoveryInformation), visible via the BitLocker Recovery tab of the computer’s properties in Active Directory Users and Computers.
4. A printout, a text file or a USB drive
At activation, Windows offers to save the key. Look for a file often named « BitLocker Recovery Key … .txt » (on an external disk, a USB drive or cloud storage), a printed sheet, or a key stored on a USB drive.
Step 3: back up your key right now (the anti-headache move)
If Windows still boots, take five minutes to multiply the backup copies. Go to Control Panel → BitLocker Drive Encryption → Back up your recovery key. Windows offers four options; use at least two:
- Save to your Microsoft account (the handiest, findable online anywhere).
- Save to a file (to place on a USB drive or external disk, never on the encrypted drive itself).
- Print the key (a paper copy stored in a safe place).
On the command line, you can also list and back up the protectors:
manage-bde -protectors -get C:This command displays the ID and the 48-digit recovery key, which you can copy down.
Good to know: a dedicated medium — a reliable USB drive kept with your important papers — remains the most robust backup, independent of the internet and any online account.
The SanDisk Ultra 64 GB USB drive is ideal for keeping your recovery keys and creating a Windows repair media.
Check the SanDisk Ultra 64 GB USB drive price on Amazon
As an Amazon Associate, Wanda-techs earns from qualifying purchases. This affects neither our independent analysis nor the price you pay.
Step 4: create (enable) BitLocker and generate a key
Want to encrypt a PC that isn’t yet? Here’s how to enable BitLocker and immediately get a recovery key.
On Windows Pro, Enterprise or Education: Control Panel → BitLocker Drive Encryption → Turn on BitLocker. The wizard asks how to save the key — choose several locations (Step 3) — then starts encryption.
On Windows Home: you don’t have full BitLocker, but device encryption can be enabled in Settings → Privacy & security → Device encryption, provided you’re signed in with a Microsoft account (the key is then saved there automatically).
Warning: before enabling encryption, make sure you’ve noted the key. And never store the only copy of the key on the drive you’re encrypting.
Step 5: special cases and troubleshooting
- Local account, no online key: if the PC was ever connected to a Microsoft account, check it at
aka.ms/myrecoverykey. Otherwise, only physical media (USB, paper) can hold the key. - The key is refused on screen: the recovery screen often uses a QWERTY layout. Enter only the digits (the numeric keypad works), dashes being automatic.
- Several encrypted disks or volumes: each has its own key. Check the displayed Key ID to pick the right one.
- You want to stop the key prompts: suspend BitLocker before a sensitive operation (update, BIOS change) with
manage-bde -protectors -disable C: -RebootCount 2, or fully decrypt the disk via Turn off BitLocker if you no longer need encryption. - Company: enable automatic backup to Entra ID / AD via a Group Policy, so every key is centrally archived as soon as it’s activated.
Step 6: avoid getting locked out in the future
Three simple habits are enough:
1. Back up the key to at least two media (Microsoft account + USB/paper).
2. Suspend BitLocker before a major Windows or firmware update.
3. Check once a year that you still know where your key is — a test worth its weight in gold on the day of an incident.
Why does Windows suddenly ask for the key? (the triggers)
Understanding what causes the recovery screen helps you avoid it. BitLocker asks for the key as soon as it detects a change that might indicate tampering. The most common triggers:
- A Windows update touching startup (Secure Boot, boot manager), like some recent cumulative updates.
- A BIOS/UEFI update or a change to its settings (boot order, Secure Boot, TPM enabled/disabled).
- A hardware change: adding/removing a disk, replacing the motherboard, sometimes an expansion card.
- A TPM reset or clearing of its data.
- Several failed startup PIN entries, or plugging/unplugging a boot device.
Tip: before one of these operations (especially a BIOS update or a big Windows update), suspend BitLocker; you’ll avoid the key prompt at restart.
Manage BitLocker with PowerShell (useful in a company)
PowerShell offers quick control, ideal for checking or automating. Open PowerShell as administrator:
Get-BitLockerVolumeThis command lists each volume, its encryption state and its protectors. To display the ID and recovery key of a volume:
(Get-BitLockerVolume -MountPoint " C: ").KeyProtectorIn a managed environment, you can send the key back to Entra ID / Azure AD to archive it centrally:
BackupToAAD-BitLockerKeyProtector -MountPoint " C: " -KeyProtectorId " {ID} "Replace {ID} with the recovery protector’s ID obtained in the previous command. It’s the most reliable way to ensure no key is left un-backed-up across a fleet.
Good to know: to keep a readable offline copy, export the key to a text file then print it to PDF that you store in an encrypted password manager. You thus combine an online backup (account/Entra), a physical copy (USB/paper) and a secure digital copy.
The mistakes to avoid with your BitLocker key
A few classic errors turn a minor incident into permanent data loss. Knowing them is half the protection.
Storing the only copy on the encrypted disk itself. It sounds obvious, yet many people save the .txt key file on the very drive that BitLocker protects. The day Windows asks for the key at boot, that file is inaccessible — locked behind the encryption it was supposed to unlock. Always keep at least one copy outside the machine.
Relying on memory or a single source. A Microsoft account can be deleted, a printout can be lost, a USB drive can fail. The rule is redundancy: at least two independent media, ideally three (online account, physical paper, USB drive), because the day you need the key is precisely the day one of your sources will be unavailable.
Confusing the Key ID with the key itself. On the recovery screen, Windows shows a short Key ID (a few characters). This is not the key — it only helps you identify the right 48-digit code among several. Don’t waste time trying to type the Key ID; look it up to match the correct full key.
Updating the BIOS or resetting the TPM without suspending BitLocker. This is the number-one cause of an unexpected recovery prompt. A thirty-second suspend (Step 6) spares you a stressful key hunt.
Forgetting to re-back-up after changing the key. If you rotate the key or reinstall the system, the old copies become useless. Make re-saving the new key an automatic reflex after any such change.
Warning: in a company, never let users manage their keys alone. A centralized backup to Entra ID or Active Directory is the only way to guarantee that no machine becomes a dead end when an employee leaves or a device fails.
Frequently asked questions
What’s the difference between the Windows password and the BitLocker key? The password opens your session; the recovery key (48 digits) unlocks the encrypted disk in case of a startup anomaly. They are two distinct things.
I lost the key and the PC is locked: what can I do? Without the key, there’s no workaround. Review all the sources in Step 2. Hence the importance of backing it up in advance.
Does encryption slow down my PC? On a modern SSD with a TPM, the impact is imperceptible day to day.
Can I change my recovery key? Yes: remove the old protector and add a new one with manage-bde. Then remember to re-save the new key everywhere.
Is device encryption on Windows Home the same as BitLocker? It relies on the same technology but is more limited: it turns on automatically with a Microsoft account and offers fewer management options. The recovery key works exactly the same way and is saved to your Microsoft account.
Can I disable BitLocker permanently? Yes, via Turn off BitLocker, which fully decrypts the disk. Your data then stops being protected, so only do this on a machine that doesn’t hold sensitive information.
In summary
The BitLocker recovery key is your digital lifeline. Check that your PC is encrypted (Step 1), find the key via the Microsoft account, Entra, AD or your physical media (Step 2), and above all back it up right now to several locations (Step 3). If you enable encryption, generate and copy the key immediately (Step 4). The day Windows asks for it, you’ll be ready.
Did you find your key thanks to this guide, or are you stuck on a specific case? Tell us in the comments on Wanda-techs.com.
Share this content:





Post Comment